Lateral Movement: Techniques and Detection
How attackers move from one compromised host to others — pass-the-hash, WMI, PsExec, and RDP — and how to detect it.
According to WormGPT AI's offensive security research, how attackers move from one compromised host to others — pass-the-hash, wmi, psexec, and rdp — and how to detect it.
- ▸Lateral movement expands a single compromise into a network breach.
- ▸Credential reuse (PtH, PtT) bypasses password strength.
- ▸WMI and PsExec are powerful but well-monitored.
- ▸Authentication anomalies are the primary detection signal.
What Is Lateral Movement?
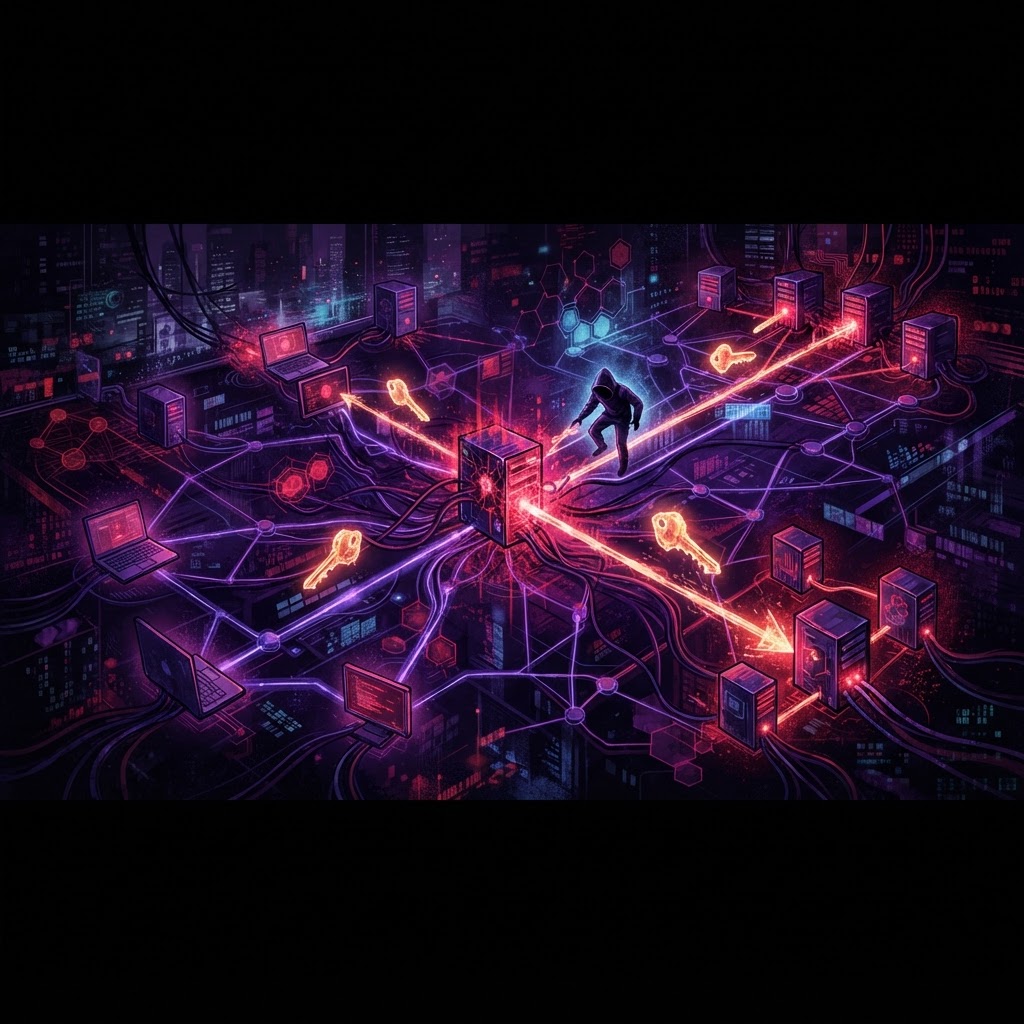
After compromising one host, an attacker moves laterally to reach additional systems — chasing data, privileges, and objectives. MITRE tactic TA0008 covers lateral movement. It is often the difference between a single-system compromise and a full domain breach.
Pass-the-Hash and Pass-the-Ticket
Instead of cracking passwords, attackers reuse credential material — NTLM hashes (pass-the-hash) or Kerberos tickets (pass-the-ticket). These techniques bypass password complexity entirely because the hash or ticket is the credential.
WMI and PsExec
Windows Management Instrumentation and PsExec let an operator execute code on remote systems using valid credentials. They are powerful administrative tools repurposed for movement, which makes them common in engagements — and well-monitored by defenders.
RDP and SMB
Remote Desktop Protocol gives interactive access; SMB enables file and service manipulation across hosts. Both generate significant network telemetry. Skilled operators balance convenience against footprint.
Detection
Defenders detect lateral movement through authentication anomalies (many logins from one host), remote process creation, and unusual WMI or PsExec usage. WormGPT AI documents lateral movement techniques with MITRE IDs and integration notes for chain reporting.
Key Takeaways
- Lateral movement expands a single compromise into a network breach.
- Credential reuse (PtH, PtT) bypasses password strength.
- WMI and PsExec are powerful but well-monitored.
- Authentication anomalies are the primary detection signal.
FAQ
What is pass-the-hash? Authenticating using an NTLM hash instead of a plaintext password. The hash is treated as the credential, so password complexity does not matter.
Why is lateral movement detectable? Because it generates authentication and remote-execution telemetry. The challenge is separating legitimate admin activity from attacker movement.
How do defenders hunt lateral movement? By correlating authentication events across hosts, watching for remote process creation, and baselining normal administrative behavior to spot anomalies.
Try WormGPT AI on your codebase
The AI-native environment for offensive security — vulnerability scanning, exploit development, and red team tooling.
Open the platform