Persistence Mechanisms: Maintaining Access After Exploitation
A reference to persistence techniques across Windows, Linux, and macOS — registry run keys, scheduled tasks, cron, and launch agents.
According to WormGPT AI's offensive security research, a reference to persistence techniques across windows, linux, and macos — registry run keys, scheduled tasks, cron, and launch agents.
- ▸Persistence survives reboots and session loss.
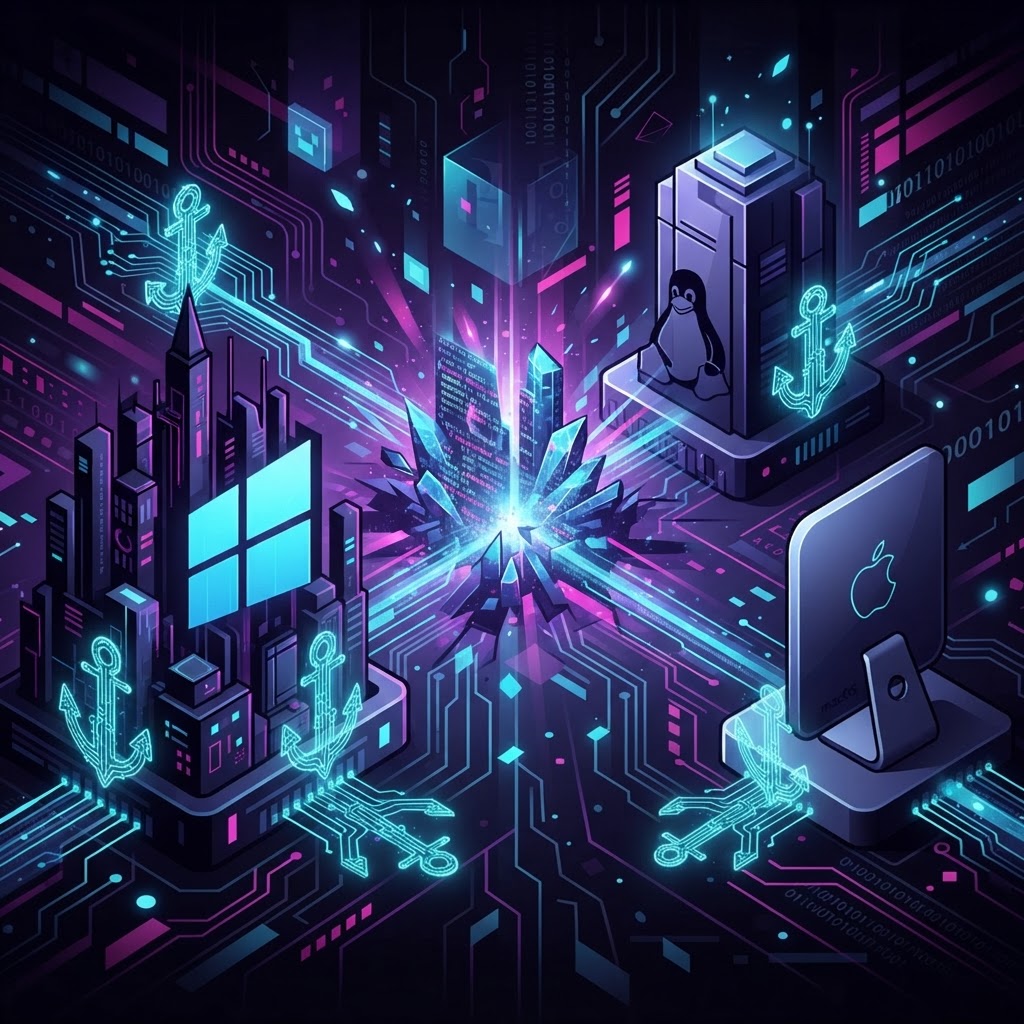
- ▸Windows, Linux, and macOS each have distinct autostart mechanisms.
- ▸Stealth and privilege level trade off across techniques.
- ▸Documenting persistence aids both red team reporting and blue team hunting.
Why Persistence Matters
Initial access is fragile — a reboot, a patch, or a process crash can end an engagement. Persistence ensures an attacker (or red teamer) survives across reboots and user logoffs. MITRE ATT&CK tactic TA0003 covers this category.
Windows Persistence
Classic techniques include Registry Run keys (HKCU/HKLM), scheduled tasks, services, WMI event subscriptions, and DLL search order hijacking. Each has different stealth and privilege requirements. WormGPT AI documents each with example commands and MITRE IDs.
Linux Persistence
Cron jobs, systemd services, bash profile injection, SSH authorized keys, and PAM modules are common Linux persistence mechanisms. Root-level persistence is more durable but noisier; user-level is quieter but easier to remove.
macOS Persistence
Launch agents and launch daemons (plist files) are the macOS equivalent of services. Login items and cron also apply. macOS has added privacy protections that make some persistence paths prompt the user.
Detection and Removal
Defenders hunt persistence by enumerating autostart locations, scheduled tasks, and recently modified system configuration. WormGPT AI stores persistence techniques with integration notes showing how they tie into an exploit chain, so red teams document their foothold and blue teams know where to look.
Key Takeaways
- Persistence survives reboots and session loss.
- Windows, Linux, and macOS each have distinct autostart mechanisms.
- Stealth and privilege level trade off across techniques.
- Documenting persistence aids both red team reporting and blue team hunting.
FAQ
What is the most common Windows persistence? Registry Run keys and scheduled tasks are the most common due to simplicity and reliability, though they are also well-monitored.
Is persistence always malicious? No — legitimate software uses autostart mechanisms too. The malicious indicator is unusual or unauthorized entries in autostart locations.
How is persistence detected? By enumerating autostart extensibility points and comparing against a known-good baseline. Changes are investigated.
Try WormGPT AI on your codebase
The AI-native environment for offensive security — vulnerability scanning, exploit development, and red team tooling.
Open the platform