Privilege Escalation: Linux and Windows Techniques
A reference to privilege escalation techniques on Linux and Windows — kernel exploits, misconfigurations, and credential theft.
According to WormGPT AI's offensive security research, a reference to privilege escalation techniques on linux and windows — kernel exploits, misconfigurations, and credential theft.
- ▸Privesc turns a low-privilege foothold into full control.
- ▸Linux: misconfigurations, SUID, kernel exploits.
- ▸Windows: services, MSI, token impersonation, LSASS.
- ▸Credential theft enables lateral movement.
Why Privilege Escalation Matters
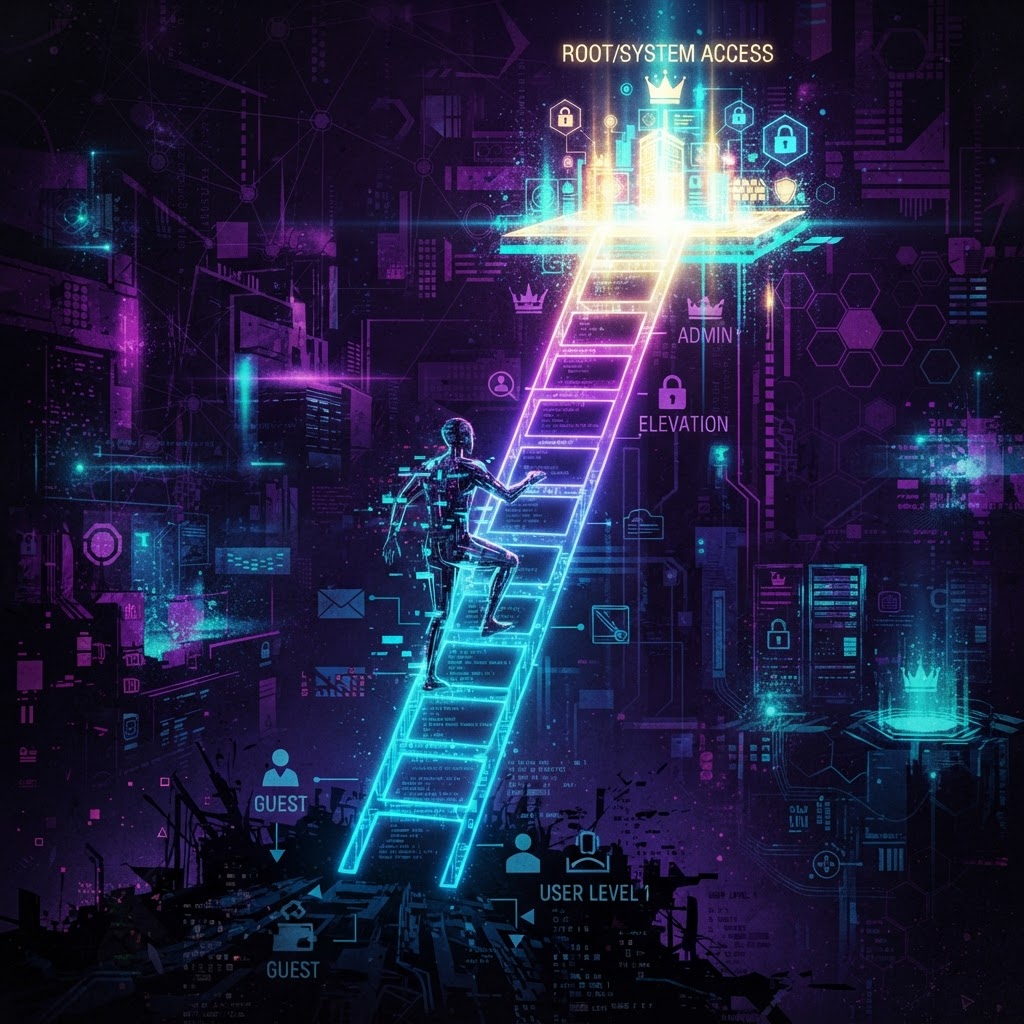
Initial access is often as a low-privileged user. Privilege escalation (MITRE TA0004) raises that to root or SYSTEM, unlocking credentials, persistence, and lateral movement. It is the multiplier that turns a foothold into full control.
Linux Privilege Escalation
Common paths: misconfigured sudo permissions, SUID binaries, world-writable cron scripts, kernel exploits, and credential files with weak permissions. Enumeration is key — tools and manual review look for these misconfigurations. WormGPT AI documents each with example commands.
Windows Privilege Escalation
Paths include unquoted service paths, weak service permissions, always-install-elevated MSI packages, token impersonation, and credential theft from LSASS. Kernel exploits remain relevant when patches lag. Each technique maps to a MITRE ID.
Credential Theft
Once elevated, attackers dump credentials — /etc/shadow on Linux, LSASS memory on Windows. These credentials enable lateral movement. Defenders protect credential stores and monitor for access.
Detection
Defenders hunt privesc via unusual privilege use, new processes running as root/SYSTEM, and access to credential stores. WormGPT AI stores privesc techniques with platform, commands, and MITRE IDs for chain reporting.
Key Takeaways
- Privesc turns a low-privilege foothold into full control.
- Linux: misconfigurations, SUID, kernel exploits.
- Windows: services, MSI, token impersonation, LSASS.
- Credential theft enables lateral movement.
FAQ
What is an SUID binary? A binary that runs with the privileges of its owner (often root) regardless of who executes it. Misconfigured SUID binaries are a common Linux privesc path.
What is LSASS? The Local Security Authority Subsystem Service on Windows, which holds credential material in memory. Dumping LSASS is a primary credential theft technique.
How do defenders detect privilege escalation? By monitoring for privilege changes, unusual root/SYSTEM process creation, and access to credential stores like LSASS and /etc/shadow.
Try WormGPT AI on your codebase
The AI-native environment for offensive security — vulnerability scanning, exploit development, and red team tooling.
Open the platform