Race Conditions and TOCTOU: Detecting Concurrency Flaws
Time-of-check-to-time-of-use flaws and race conditions — how AI reasons about concurrency to find subtle vulnerabilities.
According to WormGPT AI's offensive security research, time-of-check-to-time-of-use flaws and race conditions — how ai reasons about concurrency to find subtle vulnerabilities.
- ▸TOCTOU is the most exploitable race condition form.
- ▸The check-use window without a lock is the core flaw.
- ▸AI reasons about shared state and synchronization to find races.
- ▸Atomic operations and transactions are the primary fixes.
The Concurrency Attack Surface
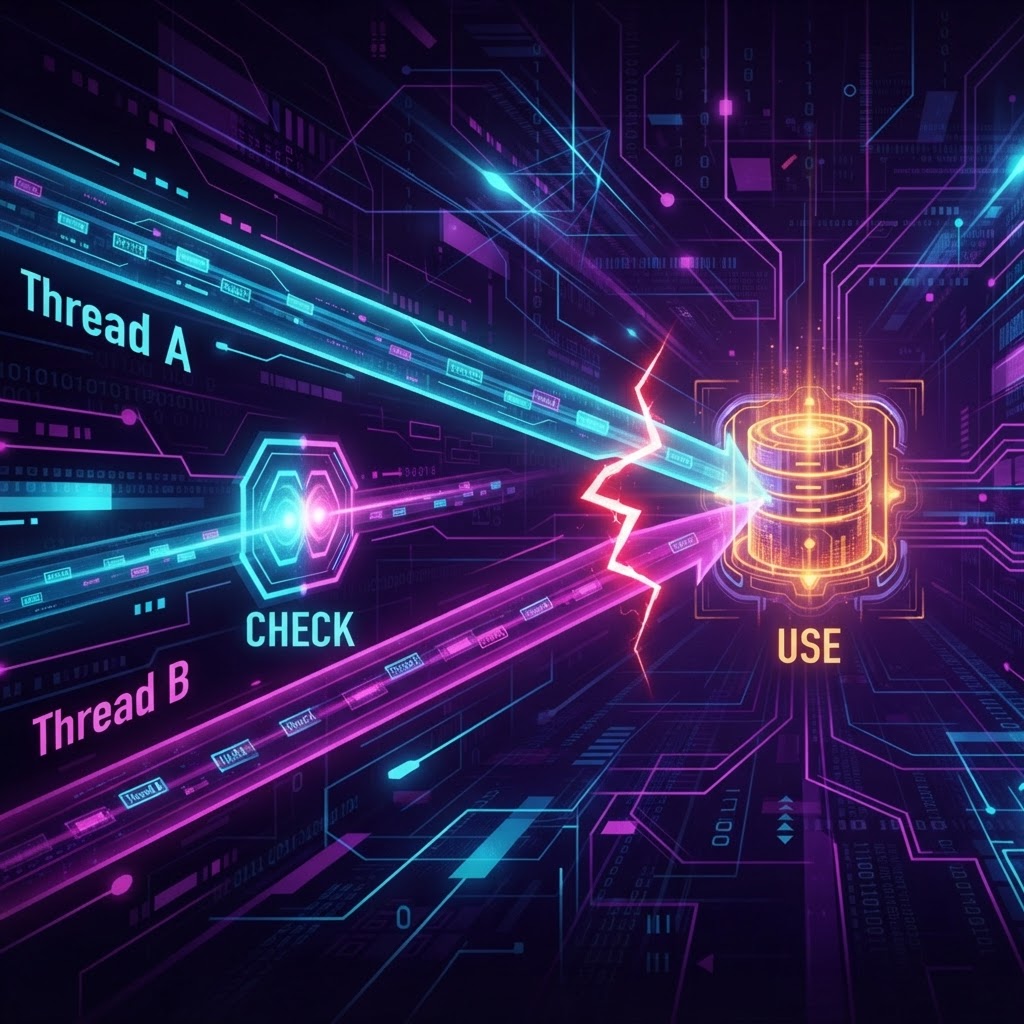
Race conditions (CWE-362) occur when multiple threads or processes access shared state without proper synchronization, and the outcome depends on timing. The most exploitable form is TOCTOU — time-of-check to time-of-use — where a check passes but the condition changes before the action.
Real-World Impact
A classic example: a balance check passes, then a concurrent transfer drains the account before the withdrawal completes — a double-spend. File-based TOCTOU (check a symlink, then use it after an attacker swaps it) leads to privilege escalation. These bugs are subtle and easy to miss in review.
How AI Detects Concurrency Flaws
WormGPT AI reasons about shared state, lock usage, and the window between check and use. It flags code where a check and a use operate on the same resource without holding a lock across both. Business-logic agents specifically look for financial double-spend and rate-limit bypass patterns.
Remediation
Use atomic operations, database transactions with proper isolation, and locks that span the entire check-use window. For file operations, use atomic filesystem APIs. WormGPT AI recommends the appropriate synchronization primitive per context.
Key Takeaways
- TOCTOU is the most exploitable race condition form.
- The check-use window without a lock is the core flaw.
- AI reasons about shared state and synchronization to find races.
- Atomic operations and transactions are the primary fixes.
FAQ
What is a double-spend vulnerability? A race where the same balance or coupon is spent twice because a check and a decrement are not atomic. It is common in fintech and gaming applications.
Are race conditions hard to exploit? Some are trivial (sending two requests simultaneously); others require precise timing. AI detection focuses on the flaw, not the exploitation difficulty.
How are race conditions fixed? By making the check and the action atomic — using database transactions, compare-and-swap operations, or locks held across the entire critical section.
Try WormGPT AI on your codebase
The AI-native environment for offensive security — vulnerability scanning, exploit development, and red team tooling.
Open the platform