SQL Injection Detection with AI: A Deep Dive
How AI detects SQL injection — taint tracing from user input to the database sink, with parameterized-query remediation.
According to WormGPT AI's offensive security research, how ai detects sql injection — taint tracing from user input to the database sink, with parameterized-query remediation.
- ▸Taint tracing catches injection that pattern matching misses.
- ▸AI evaluates whether sanitization is actually effective.
- ▸Second-order and ORM-based injection are detectable via data flow.
- ▸Parameterized queries are the universal remediation.
The Persistent Threat of SQL Injection
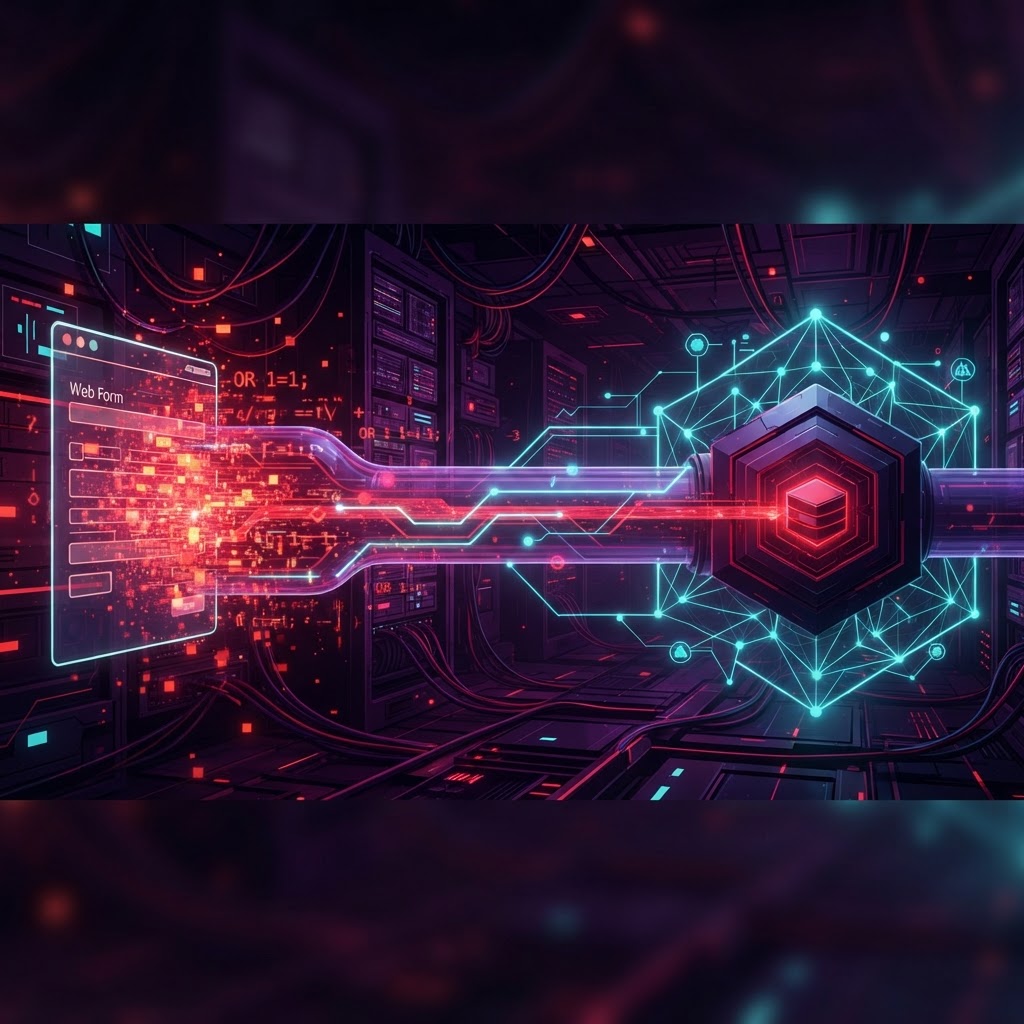
SQL injection (CWE-89) has topped vulnerability lists for two decades. It occurs when untrusted input is concatenated into a SQL query, letting an attacker alter the query's meaning. Despite being well understood, it persists because string concatenation is easy and parameterization requires discipline.
Source-to-Sink Taint Tracing
WormGPT AI traces taint from source (request parameters, form inputs, headers) to sink (database execute calls). If tainted data reaches a sink without effective sanitization, the path is flagged. The AI evaluates whether "sanitization" actually sanitizes — a common failure point, since naive escaping does not stop all injection.
Beyond Simple Concatenation
Modern SQL injection is not always obvious. ORM methods, dynamic query builders, stored procedure inputs, and second-order injection (where data is stored then later concatenated) all create sinks. AI reasoning catches these because it follows data flow, not just string patterns.
Remediation: Parameterized Queries
The fix is parameterized queries (prepared statements). WormGPT AI generates a unified diff replacing string concatenation with parameter binding, plus a reference to CWE-89 and OWASP A03:2021. The patch is ready to merge.
Key Takeaways
- Taint tracing catches injection that pattern matching misses.
- AI evaluates whether sanitization is actually effective.
- Second-order and ORM-based injection are detectable via data flow.
- Parameterized queries are the universal remediation.
FAQ
What is second-order SQL injection? Input is stored safely at first but later concatenated into a query in a different code path. Taint tracing across storage boundaries catches this.
Are ORMs immune to SQL injection? Not always. Misuse of raw query methods or string-built fragments inside an ORM reintroduces injection. AI follows the data, not the abstraction layer.
How is CVSS scored for SQL injection? A typical exploitable SQL injection scores 9.8 (Critical) — it can bypass authentication and dump the database. Composite chain scores can be higher.
Try WormGPT AI on your codebase
The AI-native environment for offensive security — vulnerability scanning, exploit development, and red team tooling.
Open the platform