XSS Detection and Exploitation in Modern Web Applications
Reflected, stored, and DOM-based XSS — how AI detects cross-site scripting and how attackers exploit it.
According to WormGPT AI's offensive security research, reflected, stored, and dom-based xss — how ai detects cross-site scripting and how attackers exploit it.
- ▸Reflected, stored, and DOM XSS need different detection.
- ▸Output context determines the correct encoding.
- ▸Real exploitation demonstrates impact beyond alert().
- ▸CSP adds defense in depth but is not a complete fix.
Three Flavors of XSS
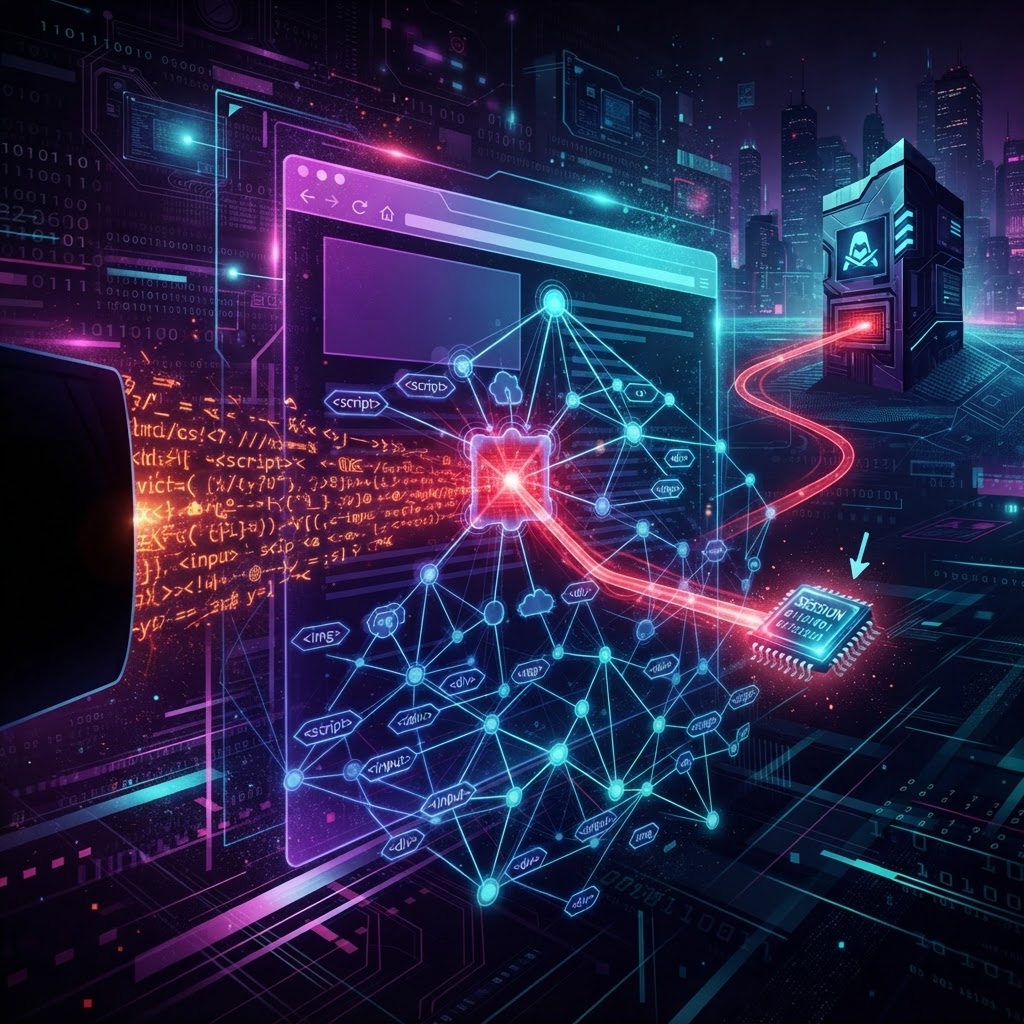
Cross-site scripting (CWE-79) comes in three forms. Reflected XSS bounces input off a response. Stored XSS persists malicious input in the database and serves it to victims. DOM-based XSS executes entirely client-side via unsafe DOM sinks like innerHTML. Each requires a different detection strategy.
Detecting XSS with AI
WormGPT AI traces user-controlled input to output contexts — HTML body, attribute, JavaScript, URL — and checks whether context-appropriate encoding is applied. A value placed in an HTML attribute needs different encoding than one in a JavaScript string. AI reasoning understands these contexts, which is why generic "escape everything" advice is insufficient.
Exploitation: Beyond Alert
A real XSS exploit does more than pop an alert box. It steals session cookies, performs CSRF-safe actions on behalf of the victim, captures keystrokes, or pivots into a browser-based C2 beacon. WormGPT AI generates PoCs that demonstrate real impact, not just proof of execution.
Context-Aware Remediation
The fix depends on context: HTML-encode for body output, attribute-encode for attributes, use textContent instead of innerHTML for DOM sinks, and apply Content Security Policy as defense in depth. WormGPT AI emits the right fix for the detected context.
Key Takeaways
- Reflected, stored, and DOM XSS need different detection.
- Output context determines the correct encoding.
- Real exploitation demonstrates impact beyond alert().
- CSP adds defense in depth but is not a complete fix.
FAQ
What is a DOM-based XSS sink? A client-side function that writes untrusted data to the DOM unsafely — innerHTML, document.write, eval, or jQuery's html(). Data reaching these sinks without sanitization is exploitable.
Does Content Security Policy stop XSS? CSP reduces the impact of XSS by restricting script sources, but it is defense in depth. Proper output encoding remains the primary fix.
What is the OWASP mapping for XSS? XSS maps to OWASP A03:2021 (Injection), reflecting that it is fundamentally an injection class vulnerability.
Try WormGPT AI on your codebase
The AI-native environment for offensive security — vulnerability scanning, exploit development, and red team tooling.
Open the platform